5 篇文章 · financial services
The SEC gives you four business days after you determine an incident is material. The hard part is the determination, and the record of how you made it.
The ESAs named their first critical ICT third-party providers. Most of the commentary focused on the providers. The more interesting consequences land on their customers.
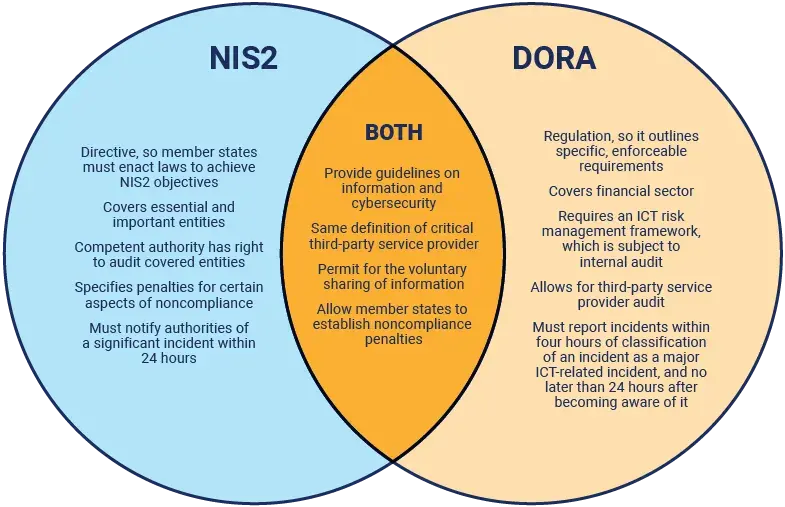
Many financial institutions are quietly running two separate compliance programmes for requirements that ask nearly the same question twice.
The Register of Information is the least discussed and most operationally demanding requirement in DORA. Here is why it keeps tripping up firms that consider themselves compliant.
With DORA now in full enforcement, financial institutions need more than paper policies - they need verifiable, audit-ready evidence that holds up under supervisory scrutiny.
关于数据完整性、合规与连续性的实用、可审计指南--发布即送达。